
For organizations operating in highly regulated industries, the challenge is no longer whether AI should be used. It is how to use it securely, how much autonomy to give it, and how quickly people and processes can adapt.
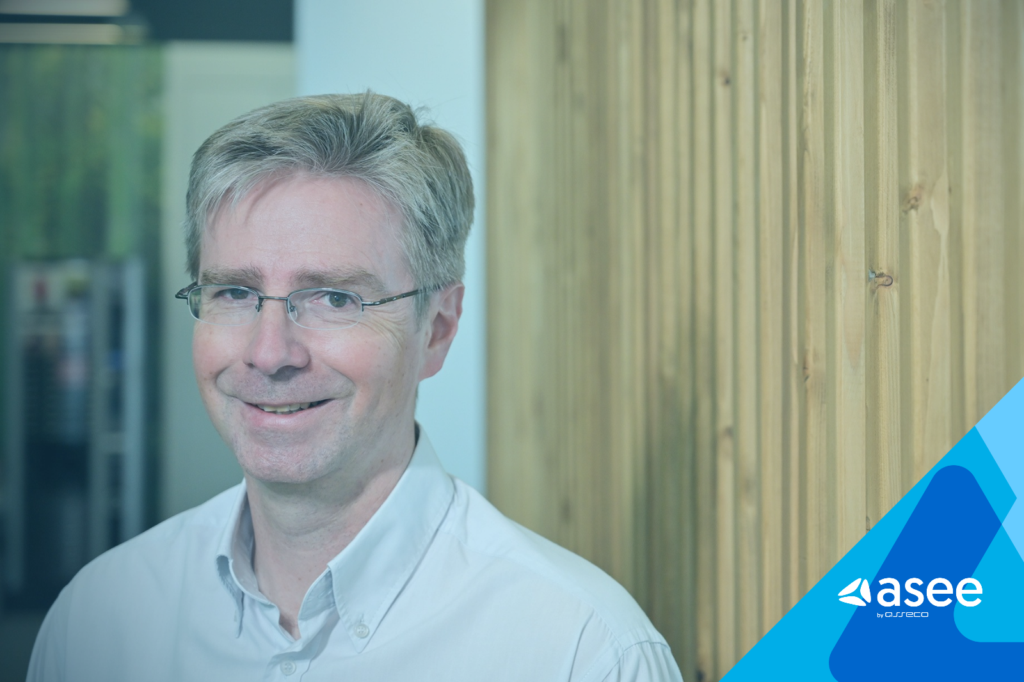
Robert Preskar, Security & Compliance Line of Business Manager at ASEE, discussed these challenges in a recent HRT Studio 4 interview (Croatian), highlighting the growing gap between the speed of AI-driven threats and the human capacity to respond.
That future may still be some way off. But the transition has already begun.
The Challenge Isn’t Finding Vulnerabilities, It’s Keeping Up With Them
Cybersecurity risks are not simply increasing in number, they are evolving faster.
Banking and financial services have been dealing with cyber threats for decades, long before the emergence of AI. Their experience has made one principle clear: organizations must protect not only themselves, but also the customers and services that depend on them.
AI is now changing the scale and speed of that challenge.
Preskar points to the dramatic increase in publicly disclosed vulnerabilities over recent years. While approximately 18,000 vulnerabilities were recorded annually around 2018, that figure had grown to around 50,000 by 2025. At the same time, the window between vulnerability disclosure and exploitation has become significantly shorter.
This creates a fundamental problem for security teams. Finding vulnerabilities is becoming increasingly automated, but analyzing, prioritizing and remediating them still requires human capacity.
The same acceleration can be seen in cyber fraud. AI-generated content has made phishing and social engineering significantly more convincing, removing one of the traditional warning signs: poor language and obvious mistakes.
“With LLMs, language is no longer a barrier.”
Deepfake technology takes this even further. Fraudsters can now imitate voices and create highly convincing communications, making it increasingly difficult for employees and customers to distinguish legitimate requests from sophisticated attacks.
At first glance, AI appears to create a level playing field: defenders have AI, and attackers have AI.
In reality, the situation is more complicated.
Commercial AI tools typically include safeguards that prevent users from carrying out certain malicious activities. A security team can use an AI model to help build a threat model, develop testing scenarios or analyze security issues, for example, but the same model may refuse to generate instructions for pentesting a system.
Criminal actors do not necessarily operate under the same constraints.
As Preskar explains, malicious versions of similar technologies available on the dark web may not have equivalent safeguards.
This does not mean that organizations are powerless. It means that cybersecurity strategies need to account for the different levels of access, autonomy and restrictions applied to AI on both sides of the conflict.
One of the most important questions surrounding AI security is not simply what an AI system can do, but what it is allowed to do.
Organizations already use identity and access management to control what individual users and software systems can access and which actions they can perform. The same principle should apply to AI.
An AI agent should not automatically have unrestricted access to corporate systems, sensitive data or business processes simply because it is technically capable of accessing them.
“AI must be restricted in the same way as any other identity in the system.”
This becomes particularly important as AI evolves beyond the traditional chatbot model. AI agents can increasingly access information, interact with users, execute tasks and potentially trigger business processes.
That makes permissions and boundaries a core part of AI security.
Organizations should therefore define what their AI systems can access, what actions they can perform, and which actions always require human approval. They should also carefully review the terms and conditions of their AI providers to understand how data is handled and whether the service aligns with their security and compliance requirements.
Technology alone will not solve the AI security challenge.
According to Preskar, organizations should establish clear internal AI policies covering which tools employees can use, for what purposes, and what information they are permitted to enter into AI systems.
Access restrictions are equally important. But there is another critical component: employee education.
Simply prohibiting employees from using AI can create a different security problem. If employees need AI to perform their work more efficiently, they may turn to publicly available or personal tools instead.
A controlled, organization-approved approach can be significantly safer.
“It is much worse not to allow employees to use AI, because they will use their own private, free version of an AI tool anyway. It is better to do it properly and limit the possibility of misuse.”
This is part of a much broader transformation. AI is changing not only cybersecurity, but also the skills organizations need.
Preskar describes the shift as one that will affect both jobs and education. Security professionals will increasingly need to understand how AI works, how to supervise it and how to integrate it into existing security processes.
For organizations in the EU, AI adoption is also taking place alongside an increasingly complex regulatory environment.
Preskar points to frameworks such as DORA, NIS2 and the Cyber Resilience Act (CRA) as important drivers pushing organizations toward stronger cybersecurity practices.
While regulatory requirements can introduce additional costs and complexity, they can also provide a framework for organizations that are still developing their security strategies.
“These regulations are pushing us toward another level of cybersecurity compared with where we were before.”
The objective should not be compliance for its own sake. Regulations can instead serve as a foundation for building more resilient organizations, particularly at a time when AI is changing the threat landscape faster than traditional security processes can adapt.
One of the biggest questions for the coming years is whether organizations will eventually be able to automate significant parts of cybersecurity defense.
Today, human oversight remains essential. AI can identify threats and vulnerabilities faster than people, but organizations still need humans to define objectives, establish permissions, validate decisions and respond when systems behave unexpectedly.
The goal, therefore, should not be to remove humans from cybersecurity overnight. It should be to gradually move humans toward higher-value decisions while allowing AI to handle increasingly large volumes of routine analysis and response.
This is particularly important because cyber resilience is not only about preventing every attack.
A well-designed and well-tested system should also be capable of recovering when something goes wrong. Regularly testing backups and ensuring that data can actually be restored can make the difference between a security incident and a prolonged business disruption.
“You might experience a cyberattack, there will be leaks, however, your business won't stop. You will recover and move on.”
That shift, from attempting to prevent every possible incident to building systems that can withstand and recover from incidents, will remain central to cybersecurity in the future.
The transition to AI-driven cybersecurity is already underway, but organizations are still learning how to manage it responsibly.
That is why knowledge sharing and collaboration are becoming increasingly important. Security professionals, technology leaders and organizations need opportunities to exchange practical experiences, understand emerging technologies and discuss where automation can genuinely deliver value.
These topics will also take center stage at Automation Summit, taking place in Split on 15–16 October. The regional conference will bring together more than 500 IT professionals to exchange knowledge and experience around artificial intelligence, automation and the technologies shaping the next phase of digital transformation.
For Preskar, events such as Automation Summit are particularly valuable at this stage of the transition.
“Technology has jumped ahead of us. Now we need to catch up with it.”
The future of cybersecurity may ultimately involve AI systems capable of defending organizations with minimal human intervention. But getting there will require more than increasingly powerful models. It will require clearly defined permissions, resilient systems, educated employees, appropriate regulation and, above all, trust built through experience.
The race between AI-powered attacks and AI-powered defense has already begun. The organizations best prepared for what comes next will be those that learn how to make AI not only more powerful, but also more controlled, resilient and secure.