
ASEE has enhanced Certiligent, its TLS certificate automation solution, with a new Certiligent Agent capability that automates certificate discovery, renewal, and deployment directly across an organization’s infrastructure.
TLS certificates serve as digital identities for websites and services, verifying their identity and protecting data such as passwords and payment card details through encryption. Like an ID card, a TLS certificate has an expiration date. Until recently, public TLS certificates could be valid for up to 398 days. However, the CA/Browser Forum, the industry body representing public certificate authorities and major browser vendors including Apple, Google, Mozilla, and Microsoft, is progressively reducing this validity period under Ballot SC-081v3.
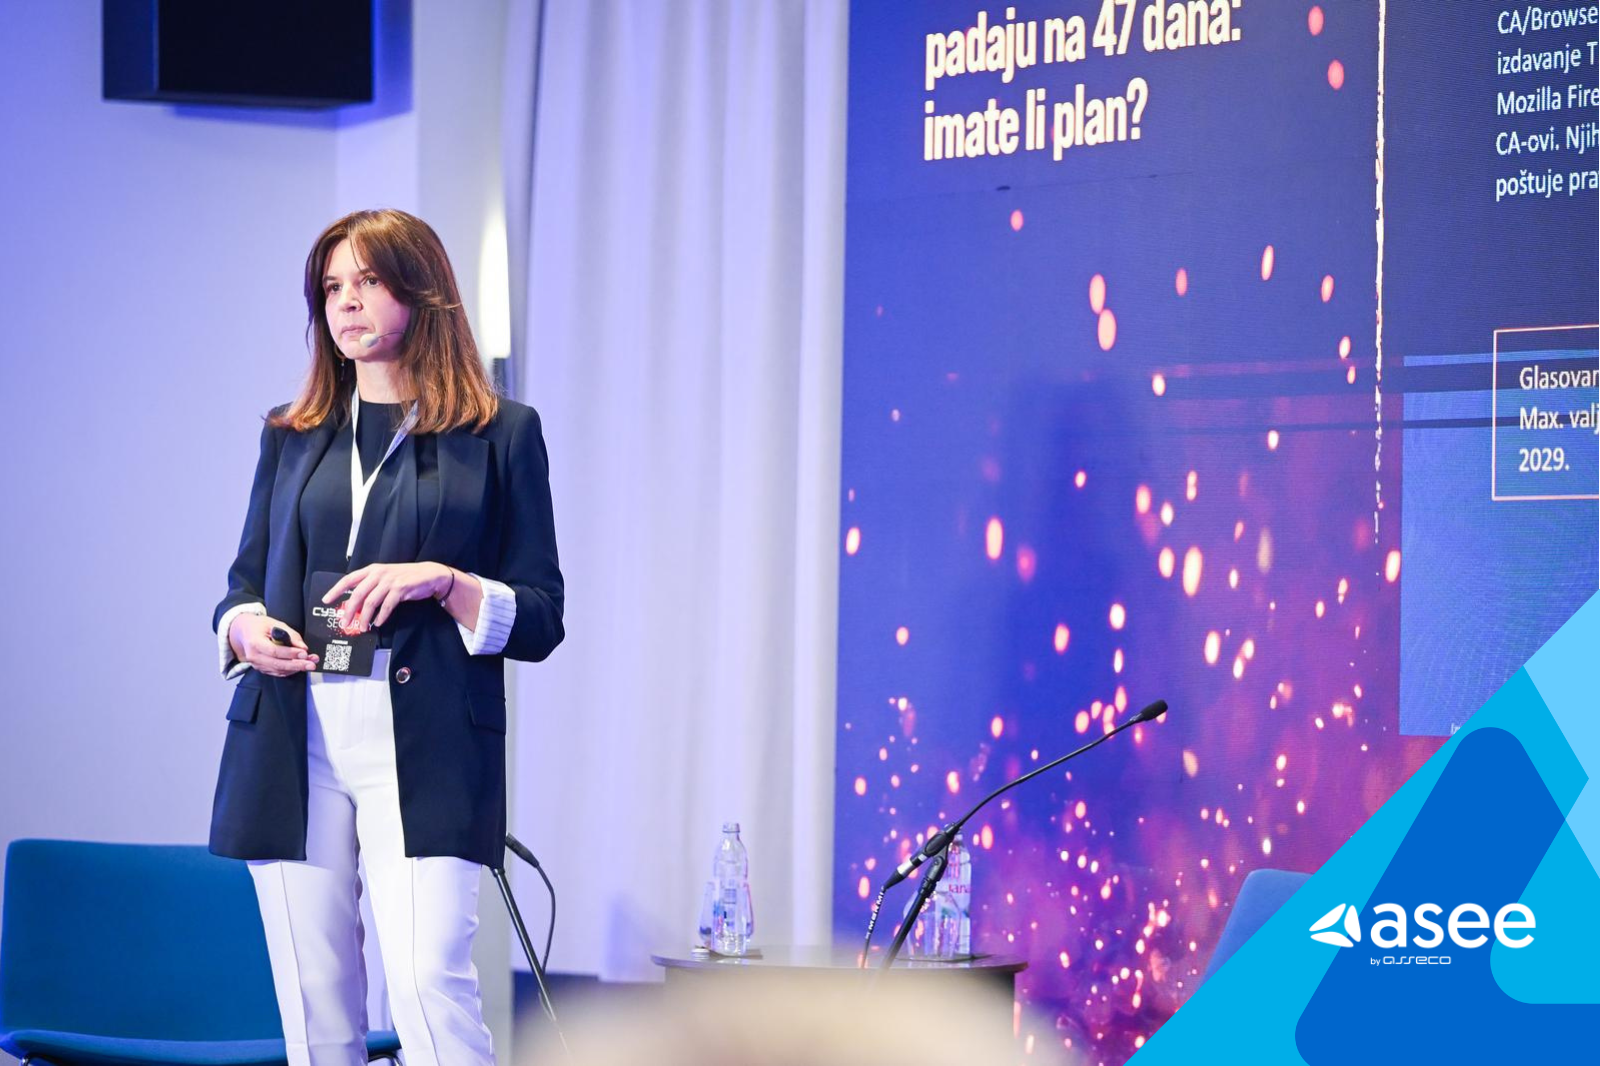
As of March 2026, the maximum validity period for TLS certificates is 200 days. This will decrease to 100 days in March 2027 and ultimately to just 47 days in March 2029.
For organizations, this means certificate renewal will occur significantly more frequently, potentially up to eight times per year instead of once. For an organization managing around 100 certificates, the additional workload could amount to as much as 1,600 hours of engineering time per year if certificate management remains largely manual.
A missed renewal can cause certificates to expire, potentially making websites, applications, and services unavailable and resulting in lost business and customer trust. As certificate lifecycles become shorter, organizations with a digital presence will need to rethink how they discover, manage, renew, and deploy their certificates.
“One of the biggest challenges is that organizations often don’t know exactly how many TLS certificates they have or where they are deployed. Certiligent Agent addresses this at the root by automatically scanning the infrastructure, ensuring that no certificate goes unnoticed,” said Robert Preskar, Director of Product and Solution Development for Security and Card Business at ASEE.
Certiligent Agent provides organizations with complete visibility and control over TLS certificates directly within their infrastructure. It automatically discovers certificates across the environment, including certificates that may have been forgotten or are no longer actively tracked, and maps them to the services and devices using them.
Once approved, certificates can enter a fully automated renewal and deployment process, eliminating manual intervention throughout the lifecycle. This automation extends all the way to the final deployment steps, including restarting services when required, helping prevent downtime and reducing the operational burden on IT teams.
The new Certiligent Agent capability builds on the existing functionality of the Certiligent platform, giving organizations a more automated approach to certificate lifecycle management as TLS certificate validity periods continue to decrease.
The progressive reduction in TLS certificate validity makes certificate lifecycle management an increasingly operational challenge for organizations of all sizes. As renewal cycles become shorter, relying on spreadsheets, manual discovery, and individual certificate owners can make it difficult to maintain visibility and prevent expired certificates.
By combining automated discovery, centralized visibility, renewal, and deployment, Certiligent helps organizations prepare for these changes while reducing repetitive work for IT and security teams.
This article is adapted from the original published on Poslovni.hr.
Learn more about Certiligent and automated TLS certificate lifecycle management